Configuration checks
Each app has a Configuration tab listing what’s set up wrong around it, worst first, each with why it matters and exactly how to fix it (with a link to the right settings page, and anything to paste: a DNS record, a header, some SQL). Periskopos only reads; every fix is yours to make.
What’s checked
Section titled “What’s checked”- The site: http:// that doesn’t redirect to https://, missing security
headers (HSTS, Content-Security-Policy, clickjacking protection,
nosniff), cookies without Secure/HttpOnly/SameSite, and files that should
never be public (
/.git,/.env,/.DS_Store), and a header that gives away the server’s version. - DNS: missing or unsafe SPF, no DMARC, no CAA.
- Connected accounts:
- GitHub: branch protection, secret scanning, Dependabot, workflow permissions (the token needs Administration: Read-only).
- Cloudflare: SSL mode (Off, Flexible, or Full without strict), Always Use HTTPS, minimum TLS, HSTS, Automatic HTTPS Rewrites, DNSSEC, and every open finding from Cloudflare’s own Security Insights. Also features that add scripts to your pages (Rocket Loader, Email Address Obfuscation, Bot Fight Mode, Web Analytics’ automatic setup) when your Content-Security-Policy blocks them, a www address that has a DNS record but answers with an error, and Email Routing whose DNS records are missing.
- Supabase: its security advisor (row level security, unsafe functions…).
- Vercel: public previews, fork protection, not linked to Git.
- Netlify: certificates, stopped builds, not linked to Git.
- Render: health check path, auto-deploy, a live app on a free instance.
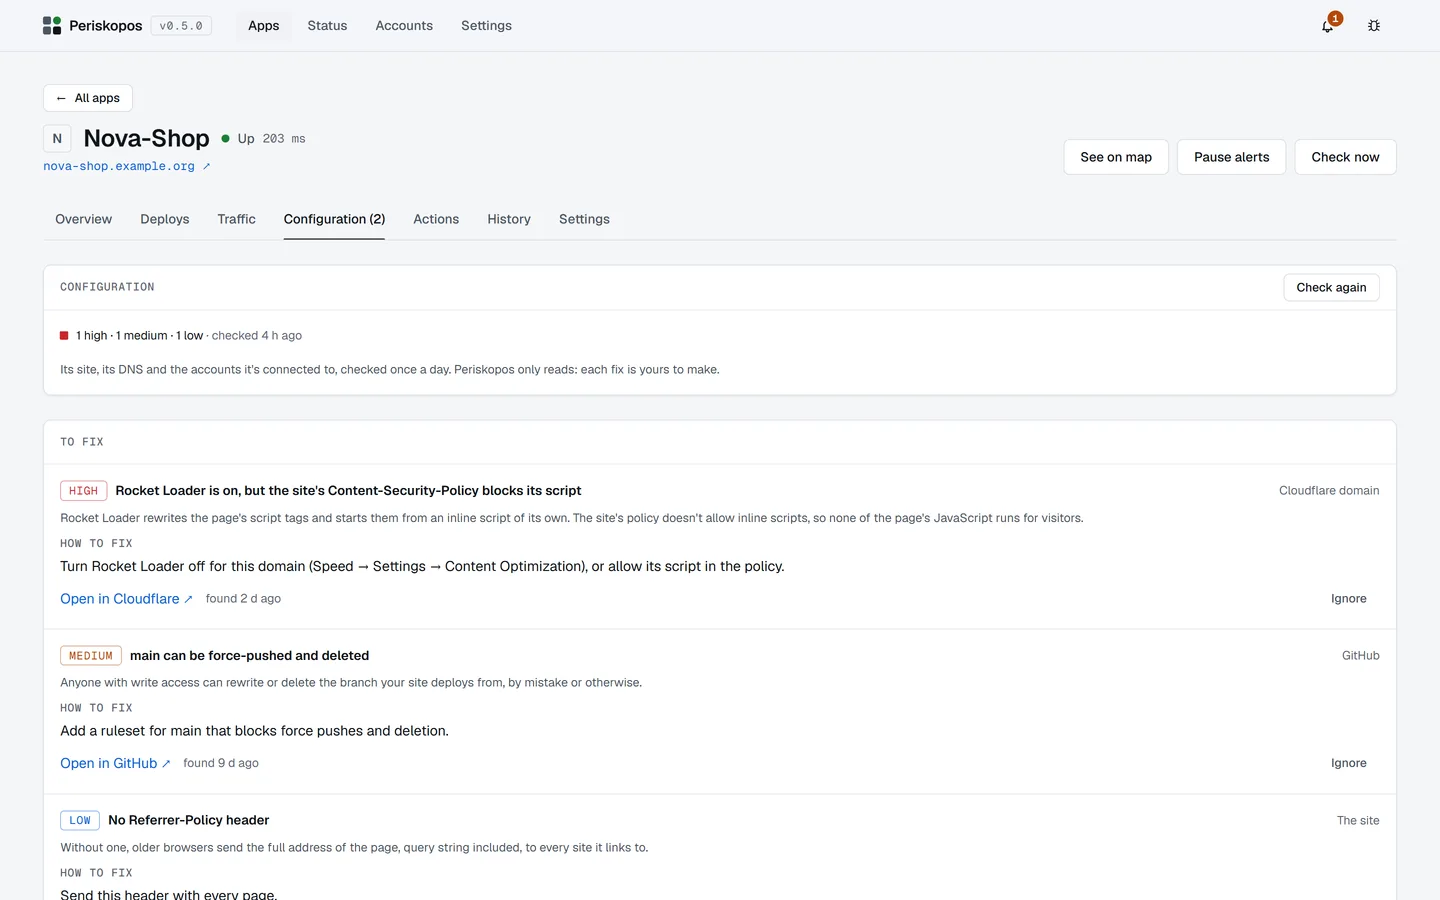
Every app is checked once a day (and on Check again). A new high-severity finding is notified; the rest wait on the tab, whose label counts what’s left to fix.
Ignore a finding that’s fine as it is: it stays ignored. What a key
isn’t allowed to read is listed as “couldn’t check”, with the permission to
add. AI assistants see the same list (get_configuration).